Snyk vs Veracode
Why choose Snyk over Veracode for AppSec?
Veracode is a legacy security tool for auditing code after it’s been compiled and adds tickets to the security backlog for developers to investigate. Snyk modernizes AppSec by automating security in the tools and workflows developers use while also providing the essential visibility, governance, and reporting that security teams need.
Snyk and Veracode comparison
Features | Snyk | Veracode |
|---|---|---|
Developer-first experience | ✔ Snyk offers real-time, actionable insights and one-click fixes that embed security early in the SDLC. Seamlessly integrates into Pull Request developer workflows with additional context to make decisions faster. | ✘ Veracode's IDEs require packaging and sending of artifacts to the Veracode static scanner, which then returns the results of scans directly into the IDE. |
Container coverage | ✔ Snyk Container provides actionable remediation advice and one-click fix for both commodity and curated base image workflows rather than just a list of vulnerabilities. | ✘ Veracode has limited container coverage. |
Real-time scanning | ✔ Snyk scans your code fast as it’s being written – averaging speeds 2.4x faster than similar solutions and increasing developer utilization of scans. | ✘ Veracode requires you to fully compile your code before you can run security scans in the context of your whole application. |
Advanced AI | ✔ DeepCode AI is a security-specific, hybrid AI and ML engine trained and updated by Snyk security researchers. | ✘ Veracode relies on Chat-GPT for code remediations, which has a higher likelihood of hallucinations due to it being general purpose. |
Embed security into the dev toolkit
Your security team is outnumbered by developers. Snyk’s real-time vulnerability scanning and automated fix suggestions in the IDE and PR workflows ensure security from the start at speed and scale.
Developer-first AppSec
Snyk finds vulnerabilities and provides fix guidance within developer tools and workflows so developers can choose a fix that works in the context of their whole application and apply it with a click, instead of providing a laundry list of vulnerabilities.
Fast, intuitive scans, no compile needed
Snyk scans code in-line as developers write and commit it, breaking free of the lengthy scan times and complex compile and upload requirements of Veracode.
Fix suggestions with full app context
Snyk provides auto-fixes and fix guidance within developer workflows so developers can choose a fix that works in the context of their whole application and apply it with a click.
Why Snyk is the best Veracode alternative
Snyk empowers developers to fix security issues with real-time scanning based on the context of their full application and policies and rules set by security teams to achieve shift-left maturity.

Accelerate developer adoption with Snyk’s IDE plugins
Snyk adds security directly into IDEs with real-time vulnerability scanning and provides actionable fix advice in line so developers can fix issues quickly and move on 82.7% of Snyk customers surveyed reported improvements in their developer processes vs. before implementing Snyk.
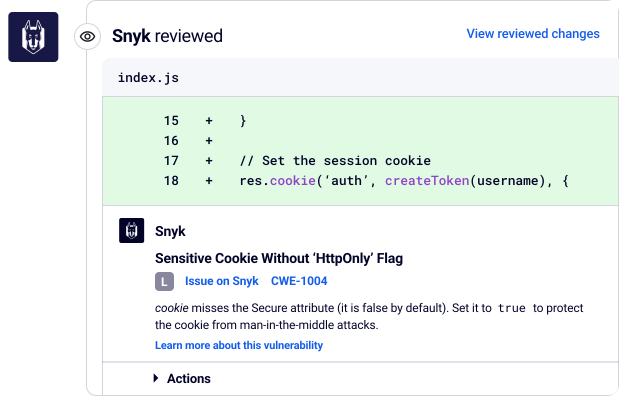
Security context embedded in your PR workflow
Snyk integrates into the PR workflow and doesn’t require developers to leave their workflow to get additional context and fix the issue. Accelerate code reviews by enabling auto-fixes within the PR workflow while providing high-context comments on vulnerability criticality, affected code, and clear remediation advice.

Complete coverage across the modern application stack
Snyk's unified platform provides comprehensive AppSec coverage through integrated native SAST, SCA, IaC, and DAST scanning, compliance tracking, real-time analytics, and enablement tools like Snyk Learn. This ensures full visibility across code, dependencies, and cloud while enabling risk prioritization and visibility throughout the entire SDLC.
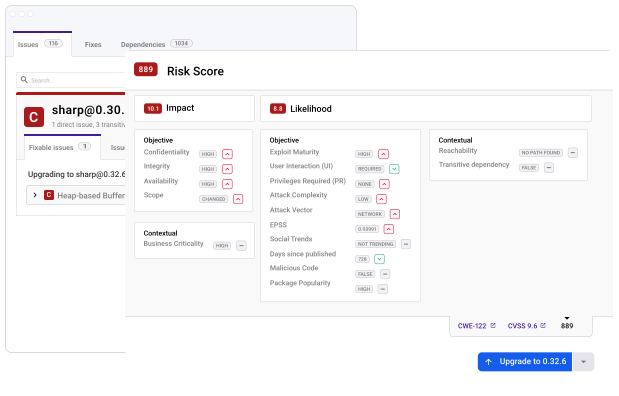
Risk-based security across your enterprise
Reduce application risk at scale with complete application discovery, tailored security controls, and risk-based prioritization.
Trusted by industry leaders
See what our customers are saying about the Snyk developer security platform.
Millions of developers build securely with Snyk


"I was really happy to have containers scanning before runtime production. People weren’t paying attention to the vulnerabilities in containers, so it has been eye opening for the organization. It truly increases awareness of those vulnerabilities and enables more automation. It’s more in line with that quality improvement mindset that the engineering teams have in their CI/CD practices."


Charlotte Townsley
Director, Security Engineering, Natera
Snyk was named a Leader in the 2024 Gartner Magic Quadrant published in April 2024 for Application Security Testing, as well as a Leader and the Customer Favorite in the 2024 Forrester Wave: Software Composition Analysis. Snyk was also named a 2024 Gartner Peer Insights Customers’ Choice for Application Security Testing, and a “vendor who shaped the year” in the IDC report for Worldwide Application Vulnerability Management Market Shares, 2023: Evolving Application Security with GenAI, Developer Experience, and a Holistic View of Risk.
Snyk customers realized savings of an average of $5.08 Million based on risk avoidance and developer efficiency gains, as well as a 70% increase in automated remediation.
Get started with Snyk
Secure your entire application stack with Snyk’s developer-first security platform.